SSO Agency · October 27, 2026
AI Workflow Security Checklist for Growing Teams
A useful AI workflow security checklist starts before anyone connects a model to customer data, a CRM, or an internal knowledge base. The highest-risk failures rarely come from the model alone. They come from unclear ownership, excessive permissions, sensitive data moving through too many systems, and automations that act faster than teams can review them.
For growth-stage companies, the goal is not to slow down AI adoption. It is to build workflows that remove manual bottlenecks without creating a new category of operational and security risk. That requires decisions across architecture, data governance, access control, vendor management, and day-to-day operations.
Why AI workflows need their own security approach
Traditional software security still applies: secure authentication, least-privilege access, encrypted data transfer, logging, testing, and incident response. AI workflows add several variables that need closer attention.
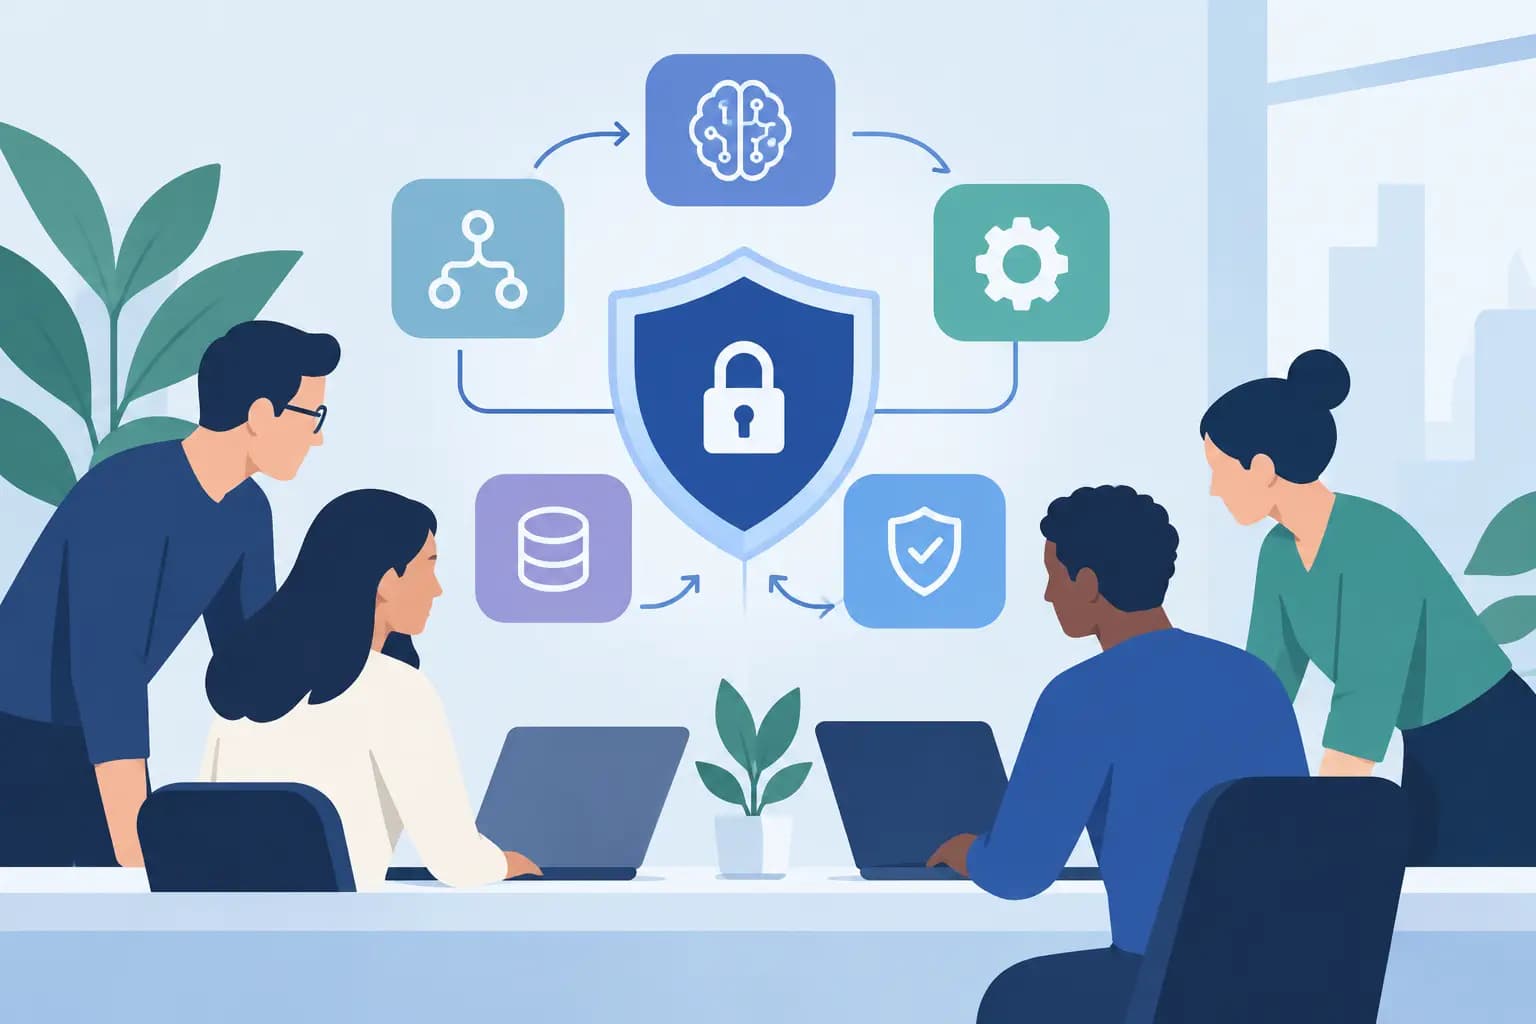
A workflow may combine a language model, an orchestration layer, APIs, a vector database, cloud storage, SaaS platforms, and custom business logic. A single prompt may retrieve internal documents, summarize account information, create a support ticket, or trigger an action in a financial or operational system. Each connection expands the potential impact of a bad configuration or an unexpected model output.
The appropriate level of control depends on the workflow. An internal drafting assistant with no system access has a different risk profile from an AI agent that can update production records or send customer-facing communications. Treating both the same either creates unnecessary friction or leaves material gaps.
AI workflow security checklist: establish the foundation
Before implementation, document what the workflow is meant to do, who owns it, what systems it touches, and what happens when it fails. This sounds basic, but it is often skipped when a useful prototype quickly becomes part of daily operations.
1. Define the workflow boundary and business owner
Write down the workflow's inputs, outputs, connected systems, users, and permitted actions. Identify a business owner who is accountable for whether the workflow remains useful and appropriate, plus a technical owner responsible for its reliability and security.
This creates a practical decision path when requirements change. Without clear ownership, teams often add new data sources and permissions incrementally until the workflow has far more access than its original purpose required.
2. Classify the data before it enters the workflow
Map the data that can be submitted to the model, retrieved from connected systems, stored for evaluation, or included in logs. Separate public information from internal business data, customer data, credentials, regulated information, and intellectual property.
The key question is not simply whether a system is secure. It is whether the workflow needs a specific data category at all. If a support triage tool can work with account tier and issue type, it may not need full customer notes, attachments, or payment details. Reducing data exposure is usually more effective than trying to secure unnecessary data after the fact.
Set retention expectations as well. Prompts, outputs, traces, embeddings, and evaluation datasets can all become sensitive records. Decide what should be retained for debugging and quality review, how long it should be kept, and who can access it.
3. Use least-privilege identities and scoped credentials
Every integration should use a dedicated service identity rather than an employee's personal account or a shared administrator credential. Scope each token to the minimum systems, records, and actions the workflow requires.
Read-only access is a strong default. If the workflow must create or update records, separate those write permissions from broad administrative privileges. Restrict access by environment where possible, so a development experiment cannot reach production customer data or production systems.
Rotate credentials, store them in a proper secret-management system, and make sure they do not appear in prompts, source code, logs, screenshots, or test fixtures. A model should never be treated as a safe place to paste credentials for convenience.
4. Separate experimentation from production
Teams need room to test AI capabilities, but experiments should not quietly become production dependencies. Use separate environments, datasets, credentials, and approval paths for prototypes and live workflows.
Synthetic or sanitized test data is preferable when it can answer the development question. Where real data is necessary for evaluation, access should be controlled and temporary. This reduces the chance that early-stage tools, unreviewed prompts, or personal API keys become embedded in a critical process.
Design controls around model behavior
AI systems can produce inaccurate, incomplete, or manipulated output. Security planning should account for that behavior instead of assuming a prompt instruction is a reliable control.
5. Treat external content as untrusted input
Documents, webpages, emails, tickets, chat messages, and uploaded files can contain instructions that attempt to redirect the workflow. This is commonly called prompt injection. A document may look harmless to a person while instructing an AI system to reveal internal information, ignore constraints, or take an unintended action.
Keep untrusted content separate from system instructions. Explicitly define what the workflow may do, validate inputs before use, and prevent retrieved content from directly authorizing actions. If the workflow processes files, validate file types, scan uploads, and place reasonable limits on size and volume.
The practical principle is simple: retrieved text can inform an answer, but it should not control the system.
6. Put human approval in front of consequential actions
For customer communication, financial changes, contract-related records, production configuration, or deletion of information, require an explicit human approval step. The workflow can prepare a recommendation, draft the change, and assemble context. A qualified person should approve the action before it is committed.
Human review does create some operational overhead. That trade-off is usually justified when an incorrect action has an external, financial, or difficult-to-reverse consequence. For low-risk internal tasks, automated execution may be appropriate once the workflow has been tested and monitored.
7. Validate outputs before systems consume them
Do not pass free-form model output directly into an API call, database query, or automated decision. Use structured schemas, field validation, allowlists, and business rules between model output and downstream execution.
For example, an AI workflow can classify a request and propose an account update. Your application should still verify that the proposed account exists, the status value is allowed, the requester has authority, and the action falls within defined limits. The model assists with interpretation; deterministic software enforces policy.
Secure the vendors, integrations, and architecture
A secure workflow is only as dependable as the services and internal systems around it. Vendor selection is not a procurement formality when the provider processes business-critical or sensitive information.
8. Review providers based on the actual use case
Assess how each provider handles data, retention, access controls, encryption, availability, incident communication, and subprocessors. Confirm the settings available for your account type, not only the capabilities described in general documentation.
Also evaluate operational fit. A model provider may be appropriate for internal summarization but not for a workflow with strict data residency, retention, or audit requirements. A no-code automation platform may speed up delivery, but it can become difficult to govern if credentials, logic, and data flows are scattered across personal workspaces.
Maintain an inventory of vendors and integrations, including the business purpose, data categories involved, system owner, and credential location. This inventory makes security reviews, diligence processes, and incident response much faster.
9. Protect knowledge retrieval and connected data sources
Retrieval-augmented workflows deserve special scrutiny because they make internal knowledge searchable through natural language. The retrieval layer must honor the same permissions users would have in the original system.
Do not assume that a single index is safe for every employee or customer. Partition data where necessary, apply access filters at query time, and test for cross-user or cross-tenant leakage. Review whether document permissions remain accurate as employees change roles, customers churn, or repositories are reorganized.
Embedding data also requires governance. Even when it is transformed, it can retain meaningful signals about the underlying content. Handle embeddings according to the sensitivity of the source material.
Make security operational, not theoretical
A checklist is useful only when it becomes part of how the workflow is shipped and maintained. Assign review points before launch, after significant integration changes, and on a regular operating cadence.
10. Log decisions, monitor exceptions, and rehearse failure paths
Capture enough information to investigate incidents without indiscriminately retaining sensitive prompts and data. Useful records may include the workflow version, user identity, source systems accessed, actions requested, approvals granted, validation failures, and final execution status.
Monitor for unusual activity such as spikes in data retrieval, repeated failed authorizations, unexpected action volume, or changes in output patterns. Define who receives alerts and who can disable the workflow quickly. A kill switch is particularly valuable for workflows that can write to systems or communicate externally.
Finally, test realistic failure cases. What happens if the model service is unavailable, an integration token expires, a user submits malicious content, or the workflow produces an invalid instruction? Teams should know whether the process fails closed, routes work to a human, or continues with reduced capability.
Build controls proportionate to the risk
The right AI workflow security checklist is not a one-time compliance exercise. It is a design discipline that lets teams automate with clearer boundaries and fewer expensive surprises. Start with the workflow that has the strongest business case, map its data and permissions, and add controls that match the consequence of getting it wrong.
That approach creates room to move from assessment to implementation with confidence: automate the work that matters, keep people accountable for high-impact decisions, and strengthen the technology foundation as adoption expands.