SSO Agency · September 25, 2026
Are AI Assistants Reliable for Business Work?
A customer support assistant confidently invents a refund policy. A sales assistant summarizes a call but assigns the wrong next step. A developer assistant produces functional code that quietly bypasses an authorization check. These are not reasons to avoid AI. They are reasons to answer the question, are AI assistants reliable, with more precision than a simple yes or no.
For business use, reliability is not a property you buy from a model provider. It is an outcome you design through the task, the data, the controls, and the person or system responsible for the final action. AI assistants can remove manual bottlenecks and improve operating speed. They can also create new operational and security risk when given authority they have not earned.
Are AI assistants reliable? It depends on the job
AI assistants are most reliable when the work has clear boundaries, trusted source material, and an easy way to verify the output. They are less reliable when the task requires current facts, nuanced judgment, complete context, or a decision with material financial, legal, or customer consequences.
That distinction matters because many teams evaluate AI tools as if they were employees. An assistant may sound confident, write fluently, and produce a plausible answer in seconds. None of that proves it has reached the correct conclusion. Language models predict useful patterns in language. They do not inherently know your company policies, customer history, system state, or strategic priorities unless those details are made available in a controlled way.
A good operating model treats AI as a capable but fallible contributor. It can prepare a first draft, classify an incoming request, summarize a document, retrieve relevant internal information, or propose a next action. It should not automatically make irreversible decisions simply because the interface makes automation feel effortless.
Reliability has several dimensions
Business leaders often use “reliable” to mean accurate. Accuracy is essential, but it is only one part of the decision. An assistant also needs to be consistent, secure, traceable, and available when the process depends on it.
A tool that gives a correct answer 95% of the time may be useful for drafting internal meeting notes. The same error rate may be unacceptable for approving wire transfers, changing customer access, or interpreting contract obligations. The business impact of an error determines the level of control required.
Consistency matters as well. If two users ask equivalent questions and receive materially different answers, the workflow may be difficult to trust or govern. Traceability matters when a team needs to understand which sources informed an answer, what instruction the assistant followed, and who approved the resulting action. Without that record, mistakes become expensive to investigate and difficult to prevent.
Where AI assistants deliver dependable value
The strongest use cases usually begin with repetitive work that already follows a recognizable process. The goal is not to automate everything. It is to prioritize the investments that reduce friction while keeping the risk proportionate to the benefit.
Internal knowledge assistance is a common example. An assistant can help employees find approved process documentation, product specifications, onboarding material, or account information spread across disconnected systems. Reliability improves when it is limited to an approved knowledge base, cites the source used, and responds with “I don’t know” when the source does not support an answer.
Workflow support is another practical area. An assistant can extract information from intake forms, classify tickets, prepare a project brief, draft follow-up emails, or summarize calls for a CRM. In these cases, the AI reduces repetitive effort, while a person retains responsibility for decisions that affect a customer or contract.
Development teams can also benefit from AI assistance in code explanation, test generation, documentation, and early-stage implementation. But generated code should move through the same peer review, testing, security scanning, and deployment controls as code written without AI. Faster production is valuable only if it does not introduce defects or technical debt faster than the team can manage them.
Where AI assistants need stronger controls
The risk rises when an assistant can take action, access sensitive data, or influence an external outcome. A conversational interface connected to a CRM, billing platform, support system, or internal database is no longer just a writing tool. It is part of the operating environment.
Customer-facing support is a useful example. An assistant can answer routine questions reliably if it works from current, approved documentation and has a clear escalation path. It should not be free to improvise policies, issue credits, or discuss account-specific information without verified permissions. The same principle applies to HR, finance, healthcare, legal, and security workflows, where an incorrect answer can create consequences far beyond an awkward response.
Autonomous actions require even more caution. Before allowing an assistant to update records, send messages, trigger refunds, provision access, or modify production systems, define the action limits explicitly. Start with recommendations or draft actions. Add human approval for higher-impact steps. Expand authority only after the process has been tested against real exceptions, not just ideal examples.
This is not bureaucracy for its own sake. It is how teams scale without introducing unnecessary complexity. Clear controls make it possible to identify where the assistant is genuinely useful and where the existing process needs more structure before automation can be trusted.
Build reliability into the implementation
Reliable AI implementations begin with a business problem, not a chatbot. If the objective is vague - “we need AI” - the result is often an impressive demo with unclear ownership and limited operational value. A better starting point is a measurable constraint: slow ticket triage, inconsistent sales follow-up, manual document processing, delayed reporting, or an overloaded internal support team.
From there, define what a good outcome looks like. This may include response accuracy, time saved per request, percentage of work handled without escalation, reduction in rework, or the number of exceptions caught before they reach a customer. Metrics should reflect quality as well as speed. An assistant that closes tickets quickly by giving poor answers is not improving the operation.
Use trusted data, not open-ended assumptions
An AI assistant is only as dependable as the information and instructions surrounding it. Give it controlled access to the systems and documents it needs, and no more. Establish which source is authoritative when information conflicts. Keep ownership clear so policies, product details, and process documents do not become stale.
Data permissions deserve the same rigor as any other system integration. Consider what customer, employee, financial, or proprietary information enters prompts; where it is processed; how long it is retained; and whether it can be exposed in another user’s response. Role-based access, logging, and environment separation are practical safeguards, not optional extras.
Teams should also test for prompt injection and unexpected instructions embedded in documents, emails, or user submissions. An assistant connected to internal tools must be designed to distinguish trusted instructions from untrusted content. Otherwise, a seemingly harmless workflow can become a route to data exposure or unauthorized actions.
Keep humans where judgment matters
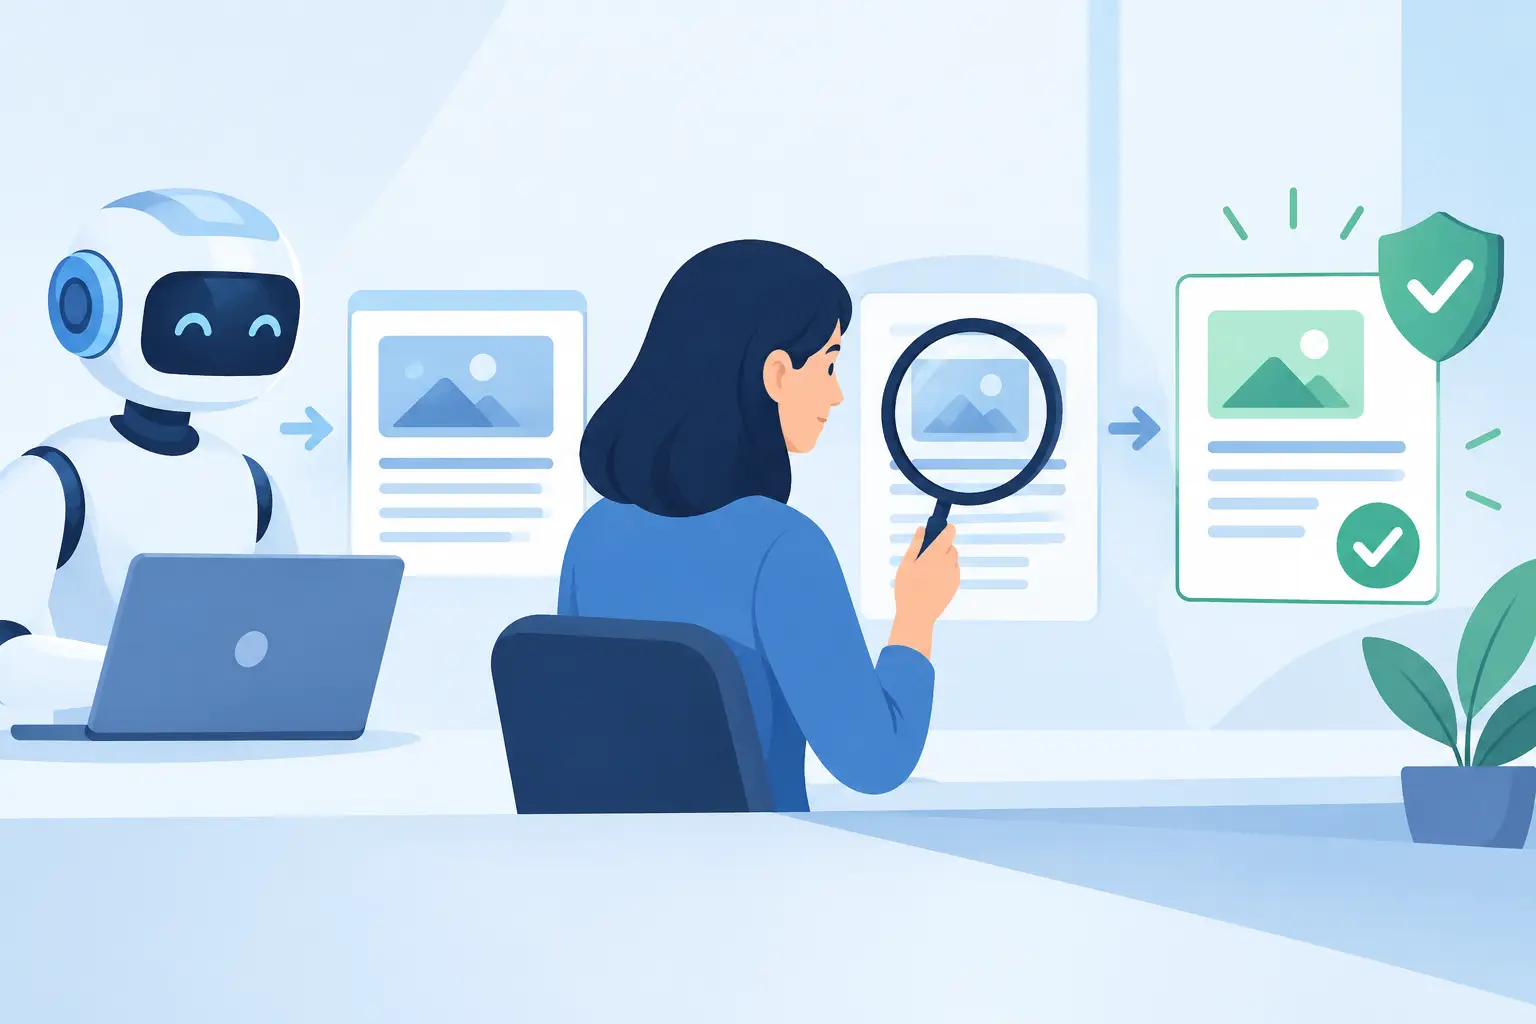
Human review does not mean every output needs the same approval process. It means the review level should match the risk. A marketing draft may require a quick editor review. A contract summary may require legal review. A recommendation to adjust pricing, close an account, or alter system access should require a named owner with authority to decide.
The most effective pattern is often graduated autonomy. First, the assistant observes and produces recommendations. Next, it drafts actions for approval. Then, for narrow and well-tested tasks, it can execute approved actions within defined limits. This gives the organization evidence before it hands over control.
Test for failure before scaling
Teams frequently test AI assistants with clean, expected inputs. Customers and operations rarely behave that way. Reliability testing should include incomplete requests, contradictory records, outdated documents, unusual phrasing, malicious inputs, edge cases, and high-volume periods.
Create a set of representative scenarios and evaluate outputs regularly as systems, policies, and models change. A workflow that performed well last quarter can drift as source data changes or integrations are updated. Monitoring should capture error patterns, escalation reasons, user feedback, and actions taken by the assistant.
When failures occur, the response should be operational, not reactive. Was the source data incomplete? Did the instruction conflict with a policy? Did the integration provide the wrong record? Was the task simply too ambiguous for automation? Turning those findings into process improvements is what moves an AI initiative from a pilot to a dependable capability.
Reliability is an execution decision
AI assistants are reliable enough to create meaningful value in many business workflows. They are not reliable enough to replace accountability, system design, or good judgment. The organizations that benefit most do not ask an assistant to solve every problem. They identify a high-value workflow, set clear boundaries, connect the right data, measure the result, and strengthen controls as adoption grows.
For founders and operators, the practical question is not whether an AI assistant can produce an answer. It is whether the surrounding process can detect a bad one before it becomes a business problem. Build that discipline first, and AI can become a useful part of a stronger technology foundation rather than another source of hidden risk.